

ThreatBook acquires CyberStrikeAI in red team push
Fri, 2nd Oct 2026 (Today)
ThreatBook has acquired the open-source AI penetration testing platform CyberStrikeAI, bringing one of the more widely used AI-led security testing tools into its red team portfolio.
Since launching in late 2025, CyberStrikeAI has attracted more than 6,600 GitHub stars and been deployed in more than 2,300 networks, according to ThreatBook. The company said it will keep the open-source version available while introducing an enterprise edition for internal security teams.
The acquisition reflects growing interest among cyber security vendors in tools that automate parts of offensive testing as defenders face faster attack cycles. ThreatBook plans to integrate CyberStrikeAI into its red team work, which simulates attacks in controlled settings so organisations can identify weaknesses before they are exploited.
ThreatBook also plans to add further controls to the open-source version to reduce the risk of misuse. It said the enterprise edition will be fully deployable inside a customer's network, with data kept on premises, a full audit trail, and permission controls for each agent action.
Open-source base
CyberStrikeAI is written in Go and has built its following through an open-source model. According to ThreatBook, the platform offers one-command deployment, a visual view of attack chains, support for multiple large language models, and a reporting function that lets users describe a target in natural language and receive a structured security assessment report.
The tool also includes more than 100 built-in templates spanning reconnaissance through exploitation. ThreatBook said this breadth has helped make CyberStrikeAI one of the most widely used AI penetration testing tools globally.
Security focus
ThreatBook framed the acquisition around the changing pace of cyber attacks and attackers' use of automation. That shift has pushed security teams to look for tools that can compress testing cycles and reveal weak points more quickly.
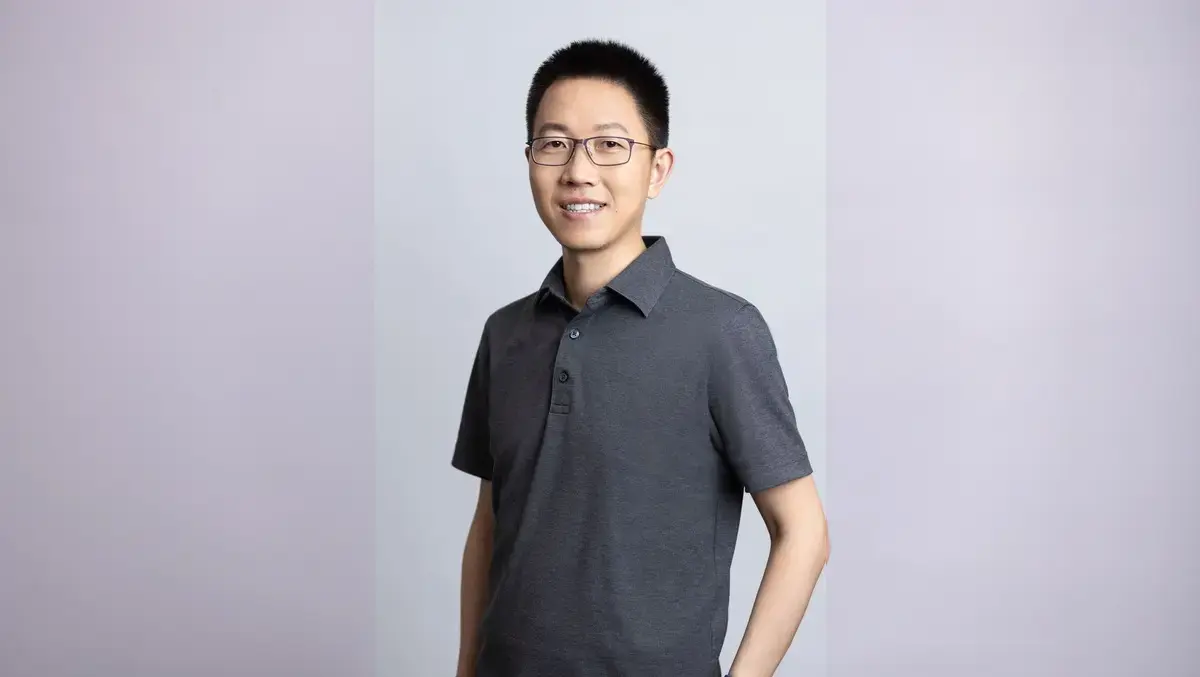
"AI attacks are now evolving far quicker than anyone could have imagined. The assumption that attackers need time to orchestrate their attacks is outdated and simply untrue. The time window that defenders once relied on to respond to attacks has been eroded by automated reconnaissance, mining and exploitation," said Xue Feng, Founder and Chief Executive Officer of ThreatBook.
ThreatBook said it intends to use the technology in enterprise security and defence scenarios rather than limiting it to specialist offensive research teams. It added that the extra controls are meant to address concerns that automated penetration testing tools could be misused without sufficient guardrails.
"Such capabilities should not be confined solely to cybercriminals, APT groups and saboteurs. They should be in the hands of defenders who are committed to building a safer world, thereby levelling the playing field and enabling defenders to think and act just as attackers do. CyberStrikeAI is a mission critical capability that helps security teams achieve this," said Feng.
Regional rollout
A trial of the enterprise edition is already available in mainland China. Wider availability across the rest of Asia-Pacific is expected next month, according to ThreatBook.
The regional focus is significant because ThreatBook has built its business around threat intelligence and security operations in Asia-Pacific. Founded in 2015, the company positions itself as a provider that combines artificial intelligence with threat intelligence across detection, triage, response and risk reduction.
Adding CyberStrikeAI to that broader portfolio gives ThreatBook a way to extend from intelligence and response into autonomous testing. For customers, the proposed enterprise version is likely to matter most in sectors that want tighter control over data location and user permissions when adopting AI tools for internal security work.
The move also highlights a broader market trend as vendors seek to package open-source security projects into commercial products with governance features. In this case, ThreatBook said those features will include on-premises deployment, audit trails, and permission controls for every agent action.
ThreatBook said it will continue investing in both the open-source and enterprise editions of CyberStrikeAI, while retaining the public version and adding further control mechanisms to prevent misuse of the technology.