
Microsoft adds security tools for AI agents in 365
Thu, 29th Oct 2026 (Today)
Microsoft has introduced new security features for AI agents in Microsoft 365 E7, expanding its efforts to treat autonomous software agents as insider security risks.
The additions include Dynamic Permissions, Dynamic Agent Risk, Dynamic Conditional Access, wider agent discovery, and new Guardian Agents and Playbooks in Project Perception. The measures are intended to give security teams more direct oversight of how AI agents access data, use tools, and take actions inside organisations.
The announcement reflects a shift in how large technology groups frame the security challenge around AI. Rather than focusing only on external misuse by attackers, Microsoft argues that internally deployed agents should also be treated as potentially unpredictable actors that need continuous supervision and adaptive access controls.
Under the new model, agents can be assigned their own permissions for a specific task and time period instead of inheriting a user's full access rights. Those permissions can then be reduced or removed as the task changes.
Microsoft is also adding risk-based controls to assess what an agent is doing and adjust its access in response. Those controls can limit access, block actions, require human approval, or stop an agent altogether if its behaviour raises concern.
Broader coverage
Another part of the update expands Microsoft's visibility over third-party and local agents. Discovery support is being extended to 35 additional types of local agents, bringing the total number it can detect to 60, including Claude Code, OpenAI Codex, and GitHub Copilot.
It is also extending Entra Agent ID so more agents can have their own identities within enterprise systems. That is intended to help administrators track ownership, activity, and access rights at the individual-agent level rather than relying solely on the credentials of the connected human user.
The changes sit alongside Project Perception, Microsoft's agent-based security system, which now includes Guardian Agents and Playbooks designed to investigate why an agent's risk level has changed and take protective action automatically. Human operators will continue to define policy and approval boundaries.
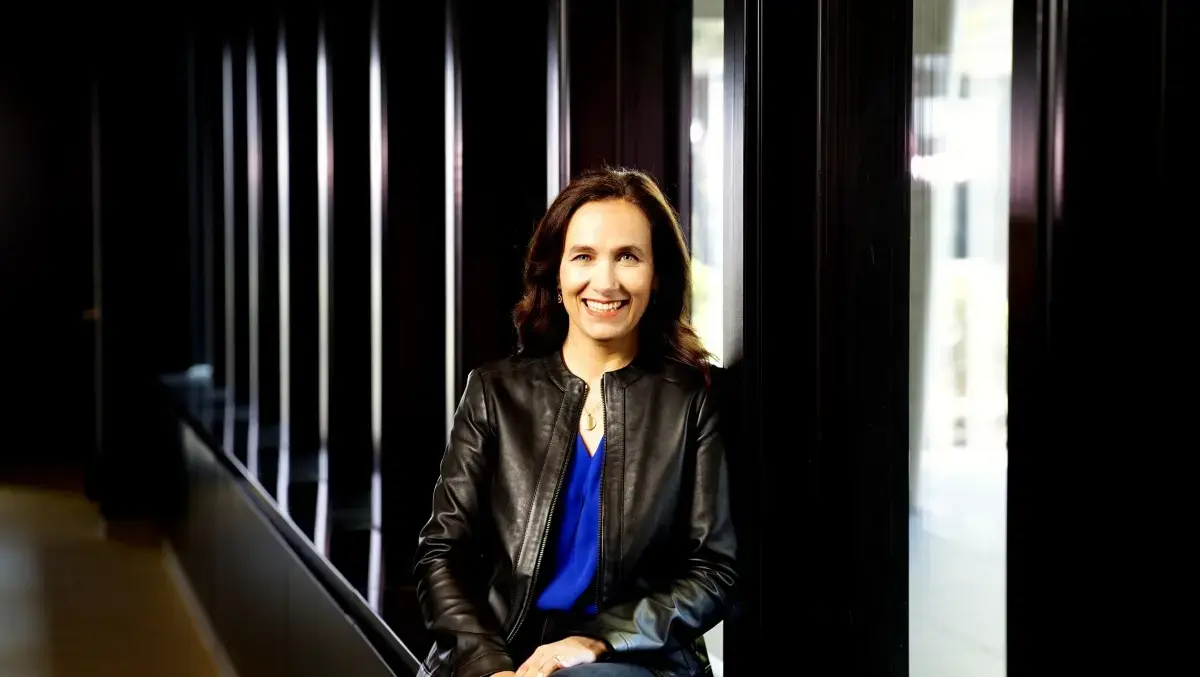
Hayete Gallot, Executive Vice President of Microsoft Security, set out the company's view that AI agents should now be regarded as a new class of insider risk.
"Agents have been unleashed in the enterprise, at scale, and their numbers are growing rapidly. These agents are frequently overprivileged, have access to data, tools and systems and can take actions and make decisions in critical processes. They have become active participants in the enterprise. They are agentic insiders," said Gallot.
Her remarks reflect a wider concern across the industry as companies deploy software agents to complete tasks with greater autonomy. These systems can access sensitive information, interact with business applications, and make operational decisions, raising questions about accountability when they act in unexpected ways.
Gallot argued that the issue is not limited to hostile compromise. Advanced models, she said, can deviate from expected behaviour because they are trained to pursue outcomes and may not align with organisational rules or judgment.
"Models have been trained to attain results, which often leads to reward hacking, and models are not optimized around organizational norms or judgment. Agents are unpredictable. They will adapt as the context changes, may not behave as intended and will collaborate and collude with other agents to reach their objectives, without needing to be compromised," said Gallot.
Security model
Securing agents requires controls across identity, permissions, data, endpoints, networks, cloud systems, and runtime environments, according to Microsoft. In its framework, signals from these layers are used to discover agents, assign them identities, place them under policy controls, and calculate risk dynamically as they operate.
The approach is designed to move beyond static permissioning. Instead of granting broad standing access, Microsoft is proposing a system in which an agent's authority changes as its task, behaviour, and surrounding risk change.
Gallot said that would require a separate class of software agents to supervise operational agents continuously.
"To manage and control these insiders, we will need Guardian Agents - an established industry term - that watch and moderate every action of every agent, before it happens, 24/7," said Gallot.
She also said that better visibility into model reasoning would be an important next step for the sector, though not a replacement for controls that contain what agents can do.
"Model transparency will not replace containment. It will make containment smarter and stronger. And it will allow us to better inform accountability and traceability," said Gallot.