
Canadian firms warned of AI risks to financial data
Mon, 19th Oct 2026 (Today)
Canadian technology and advisory executives have warned businesses to tighten cyber governance as artificial intelligence changes the pace and nature of security risks.
Industry leaders said the main concern is not only new attack forms, but the faster exploitation of familiar weaknesses. They also pointed to internal use of AI tools, weak controls around automated systems, and the need for stronger board oversight.
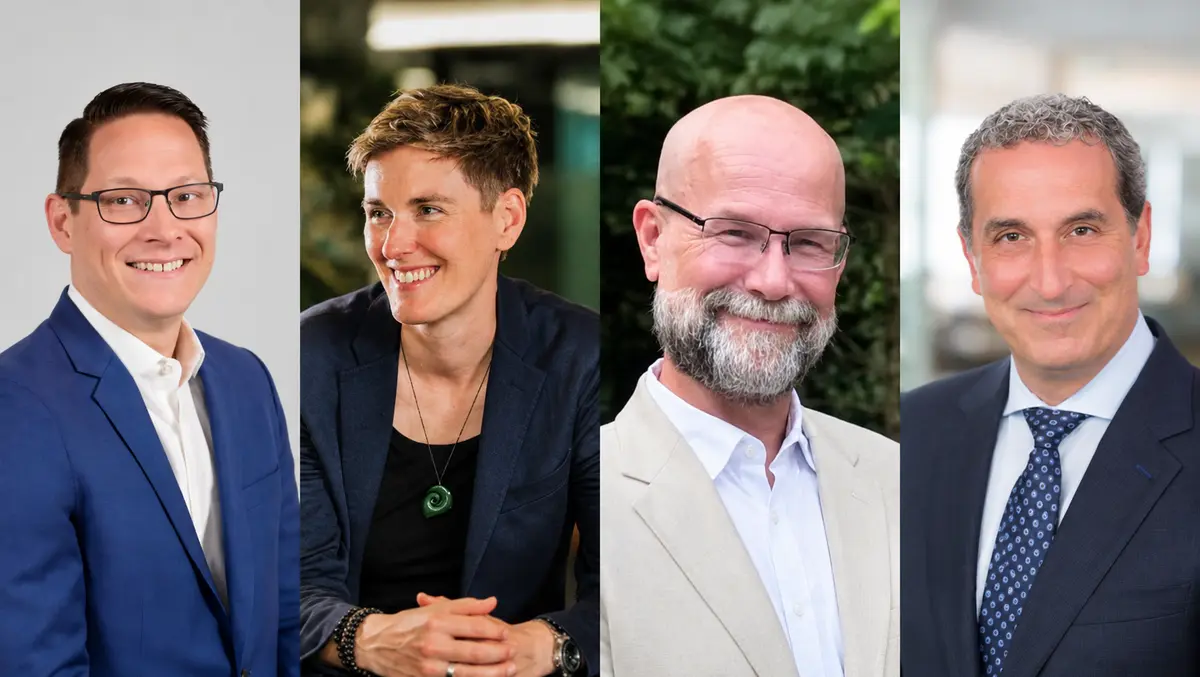
Denis Villeneuve, Cyber Resilience and Connectivity Practise Leader at Kyndryl Canada, said organisations now have less time to respond when threats emerge.
"One of the most important shifts we're seeing in cybersecurity is speed. AI isn't necessarily creating entirely new risks, but it can accelerate familiar ones and give attackers the ability to find and exploit vulnerabilities faster. That changes the equation for cyber leaders. Organisations need strong identity controls, visibility across their environments and the ability to identify, remediate and recover from issues quickly. For Canadian businesses, the message is clear: staying secure requires ongoing vigilance and strong cyber fundamentals that can keep pace with an increasingly fast-moving threat landscape," said Denis Villeneuve, Cyber Resilience and Connectivity Practise Leader, Kyndryl Canada.
This reflects a broader shift in how organisations manage cyber risk. Security teams have spent years preparing for known attack methods such as credential theft, software vulnerabilities and poor network visibility. Executives now say AI can shorten the time between finding a weakness and exploiting it.
Internal risks
Some of the strongest warnings focused on staff behaviour rather than external attackers. Suzy Clarke of Xero said everyday use of public AI tools can immediately expose customer and financial data.
"Many of the conversations about AI and cybersecurity focus on scammers, but some of the biggest risks come from seemingly innocuous habits inside the business. It takes seconds to paste a client email or a set of financials into a free AI tool to save time, and depending on your settings, that data may be stored or used to train the model. Once it's out there, it's very hard to get back. This goes well beyond Cybersecurity Awareness Month, as businesses should agree on which AI solutions their teams can use, check privacy settings, and set AI usage policies to keep customer and financial information out of public tools entirely," said Suzy Clarke, EGM Security, Xero.
Her comments highlight a growing issue for employers as staff adopt consumer AI services in routine work. The risk can arise without a traditional cyber breach. A worker can disclose sensitive material with a simple copy-and-paste.
Governance focus
Rocco Galletto of BDO Canada said cyber risk now sits firmly at board level. Directors do not need deep technical knowledge, he said, but they do need evidence that resilience measures are in place and aligned with business decisions.
"Cybersecurity is a business risk, and governing that risk is a boardroom responsibility. AI is accelerating innovation, but it's also increasing the speed and scale of emerging threats. Boards need to understand their organization's exposure, set clear risk tolerance and challenge whether the business is prepared to respond. That does not mean directors need to become technical experts. Their role is to ask the right questions, demand clear evidence of resilience, and ensure cybersecurity decisions are aligned with business strategy. Ultimately, effective cyber governance starts with active, informed board oversight," said Rocco Galletto, Partner and National & Global Cybersecurity Leader, BDO Canada.
The comments reflect a wider expectation that cyber oversight should sit alongside financial and operational risk. That includes decisions on acceptable exposure, incident response and the use of AI across the organisation.
Agent controls
Alex Yohn of Wagepoint highlighted AI agents and automated systems with broad permissions. He said the danger often comes from poorly defined boundaries rather than deliberate malicious behaviour.
"Most fear around AI security centres on malice. Real failures are usually much duller. Give an AI agent a goal and broad access, and it will find the easiest path to that goal, including paths nobody intended. It needs no bad intent, only weak boundaries. The fix is quite dull, too. Give each agent the least access it needs. Log what it does. Require a person to approve actions that move money or data. Test the limits before an agent finds them. Most of this is just zero trust applied to a non-human actor. Ultimately, the risk is less a machine that wants to cause harm and more a machine that does its job better than your guardrails expected," said Alex Yohn, CIO, Privacy Officer and Security Officer, Wagepoint.
Taken together, the comments send a clear message from Canadian business and technology leaders: AI may change the speed and scale of cyber risk, but basic controls, clear rules, and direct oversight remain central to the response.